


Agents map policy clauses to obligations, flag shortfalls and draft remediation for the policy owner
Trusted by leading financial institutions



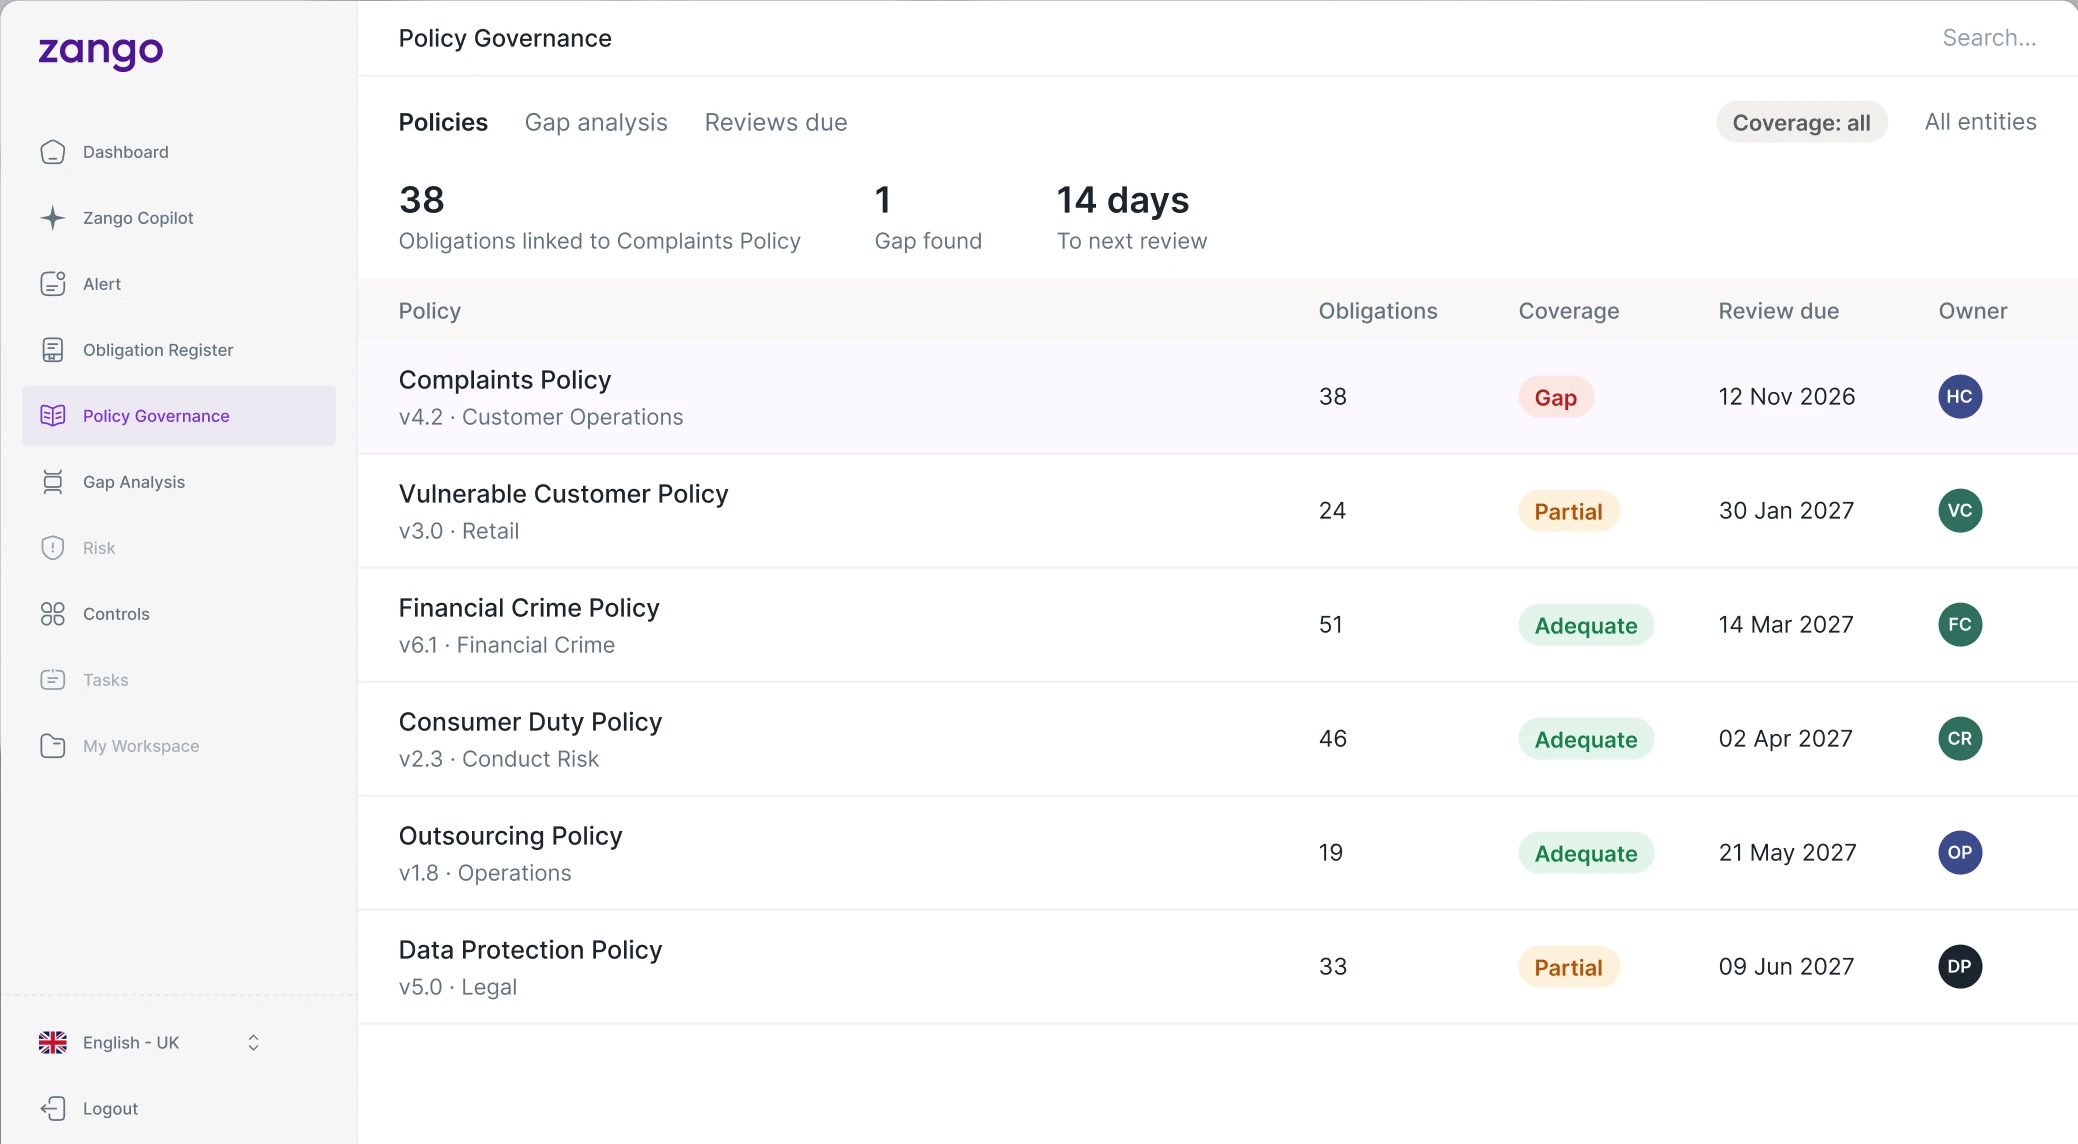
Agents link each policy to its obligations, across your entities and jurisdictions.
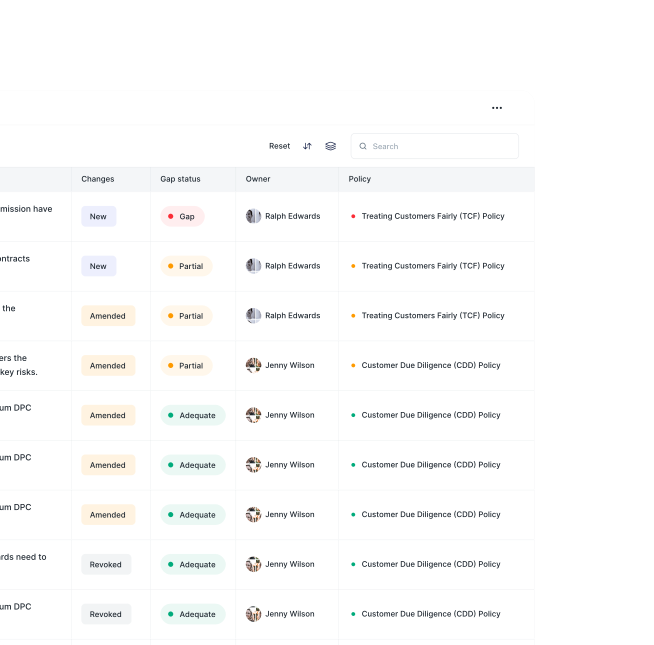
Agents match every obligation to a policy clause and rate it adequate, partial or gap, with the reasoning.
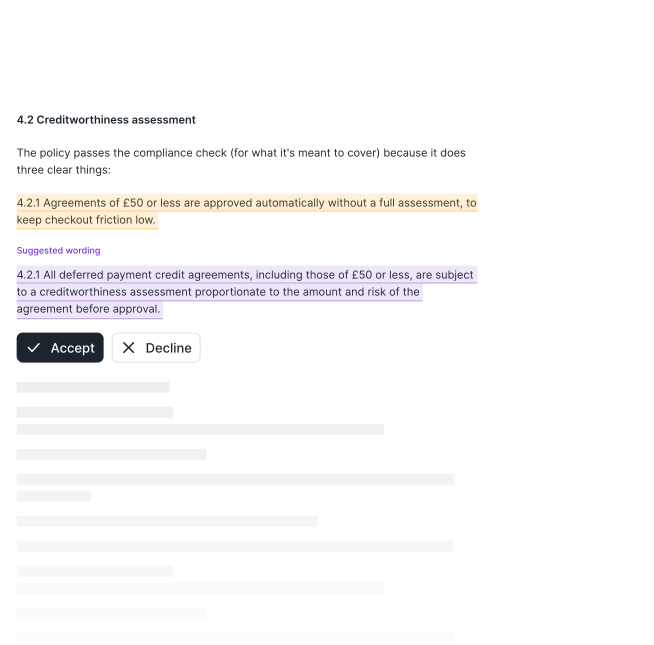
Agents draft clause wording for each gap and route it to the policy owner with an action and due date.
The owner, reviewer and approver sign off in turn, with every edit and approval recorded in version history.
“We are thrilled with how Zango has transformed our compliance processes, saving us hundreds of hours of manual repetitive work and allowing our team to focus on strategic initiatives.”
Follow a policy from its first gap analysis to the next regulatory change: mapped at clause level, assessed, remediated with sign-off and kept current.
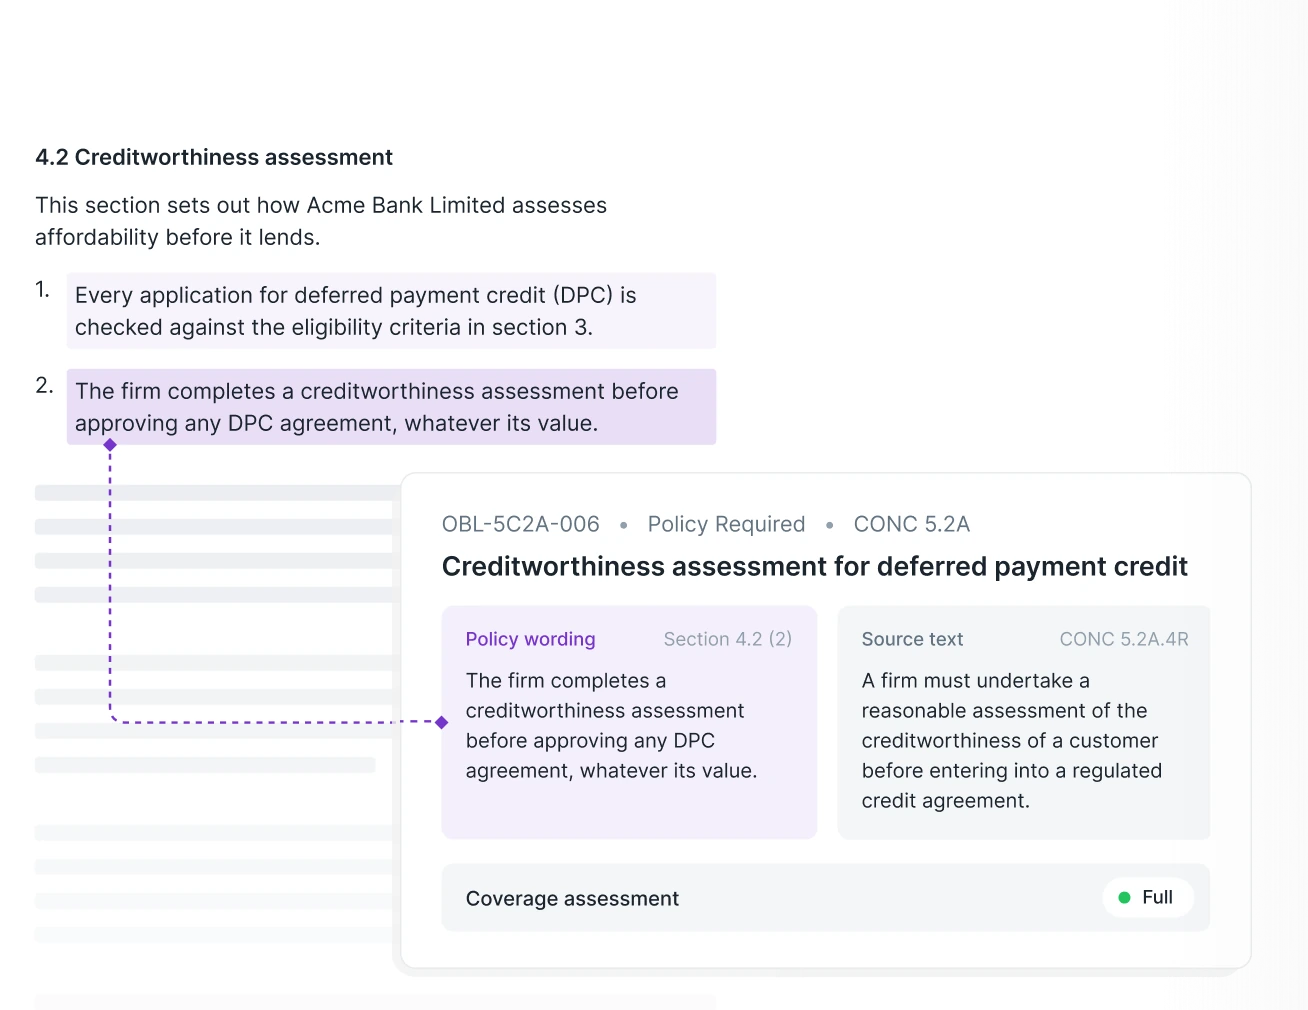
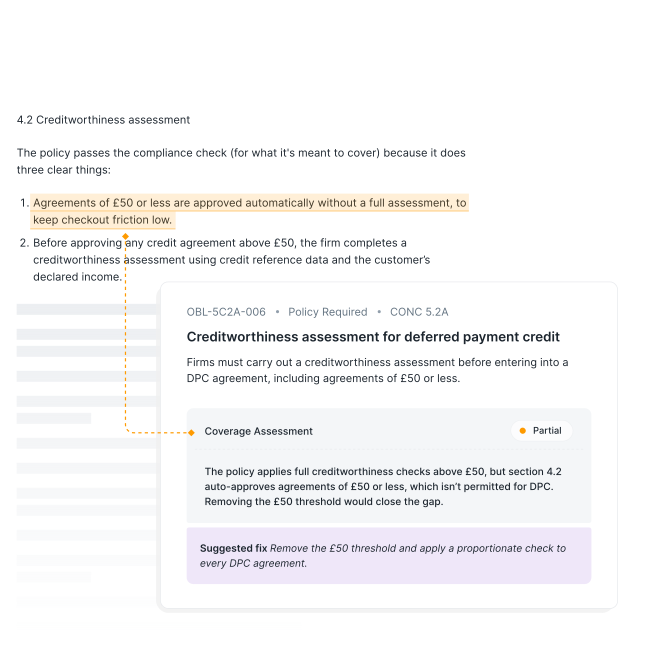
Each policy is read against every applicable obligation and matched at clause level, with source text and policy wording side by side.
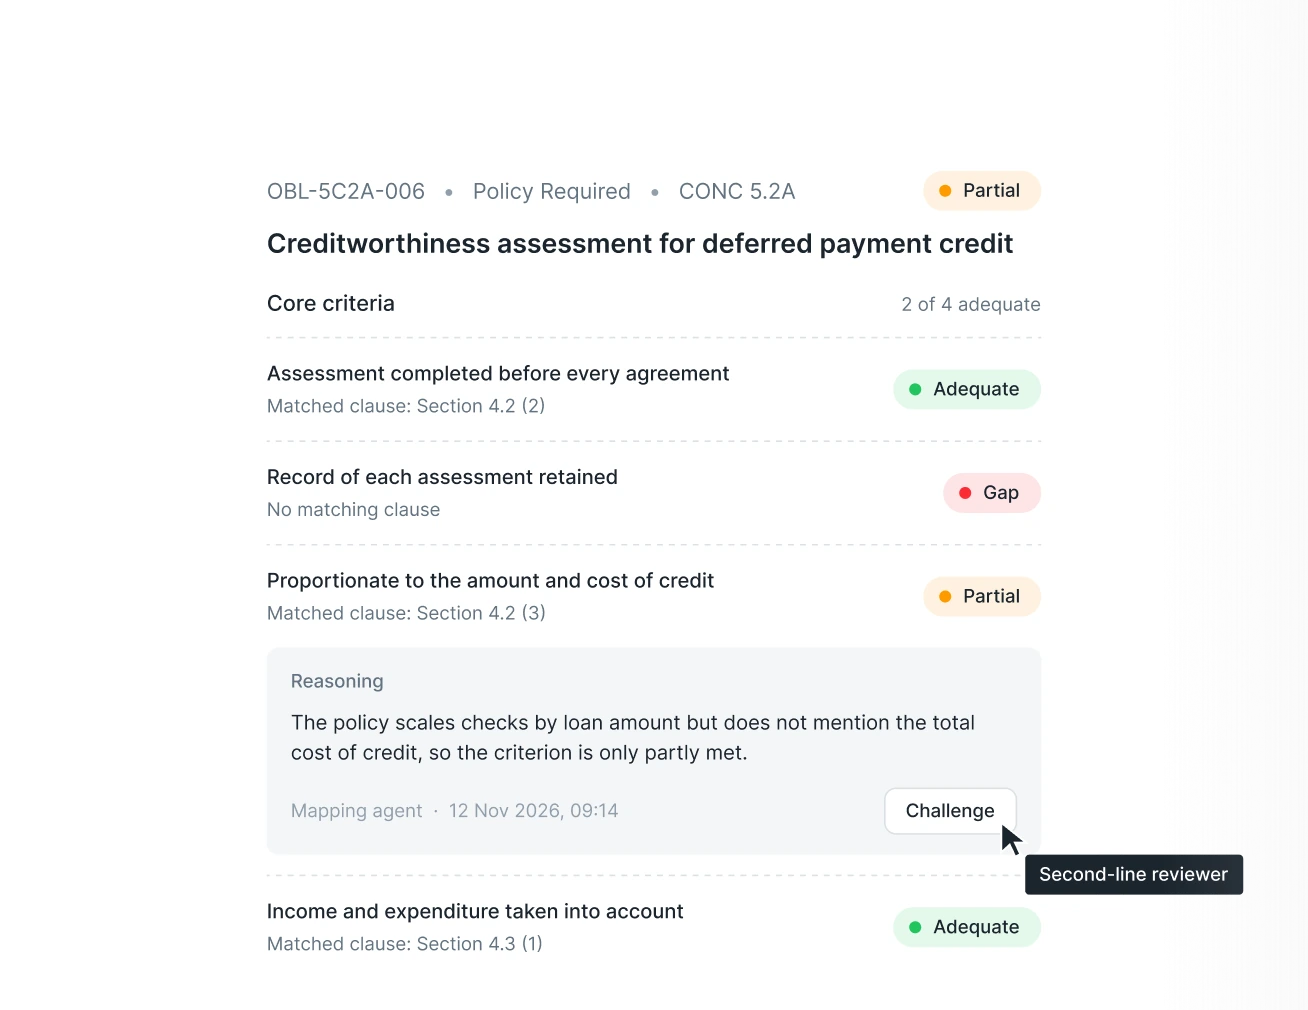
Each obligation is assessed against its core criteria, with the matched clause and reasoning recorded so second-line reviewers can challenge the call.
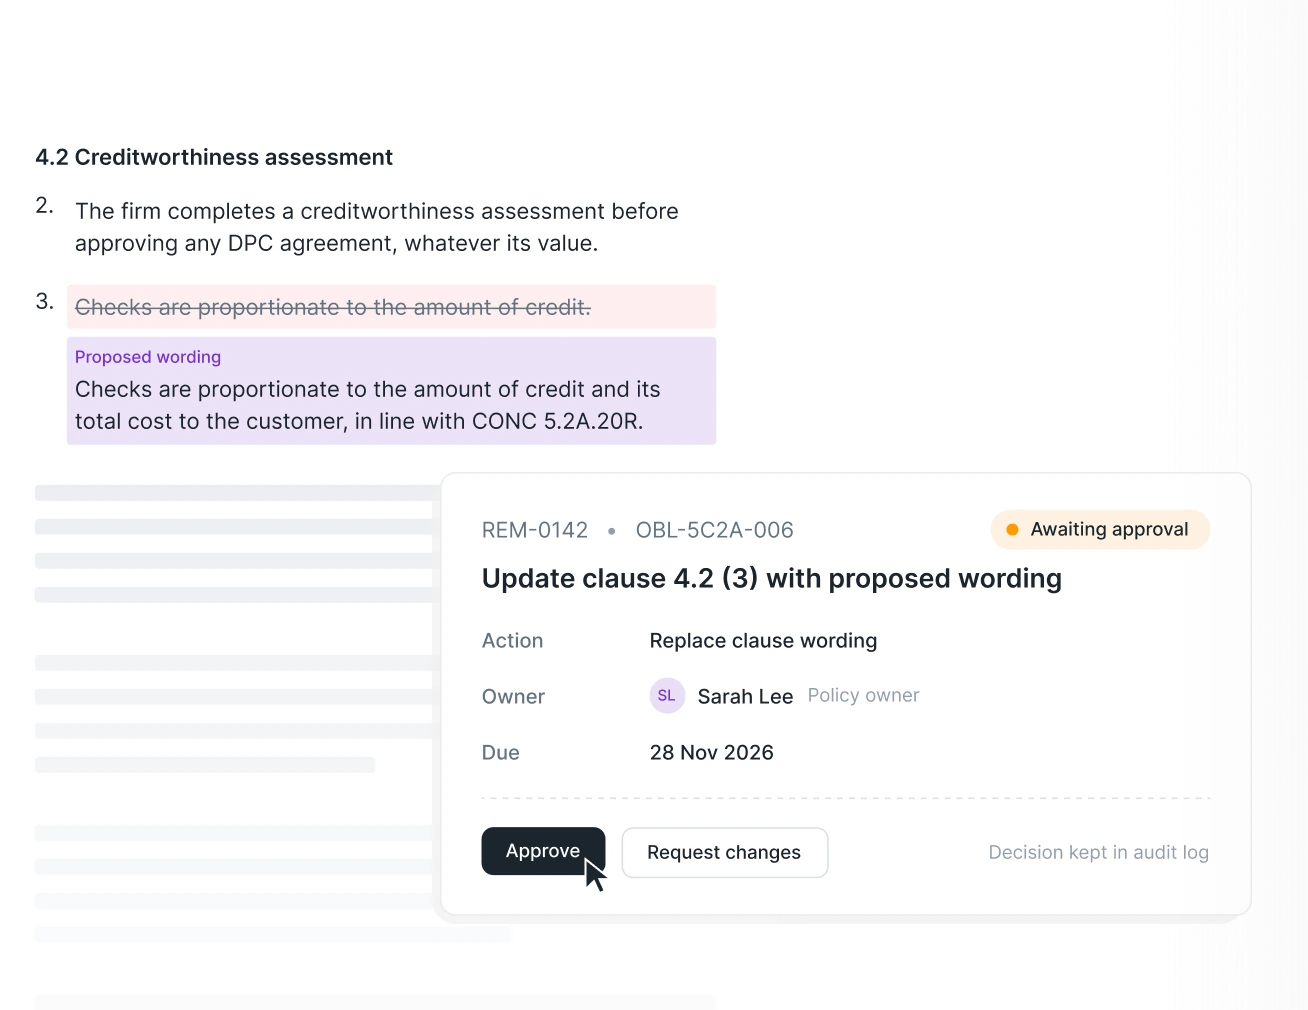
Gaps arrive with proposed clause wording, an owner and an action. Approval stays with the policy owner, and every decision is kept for audit.
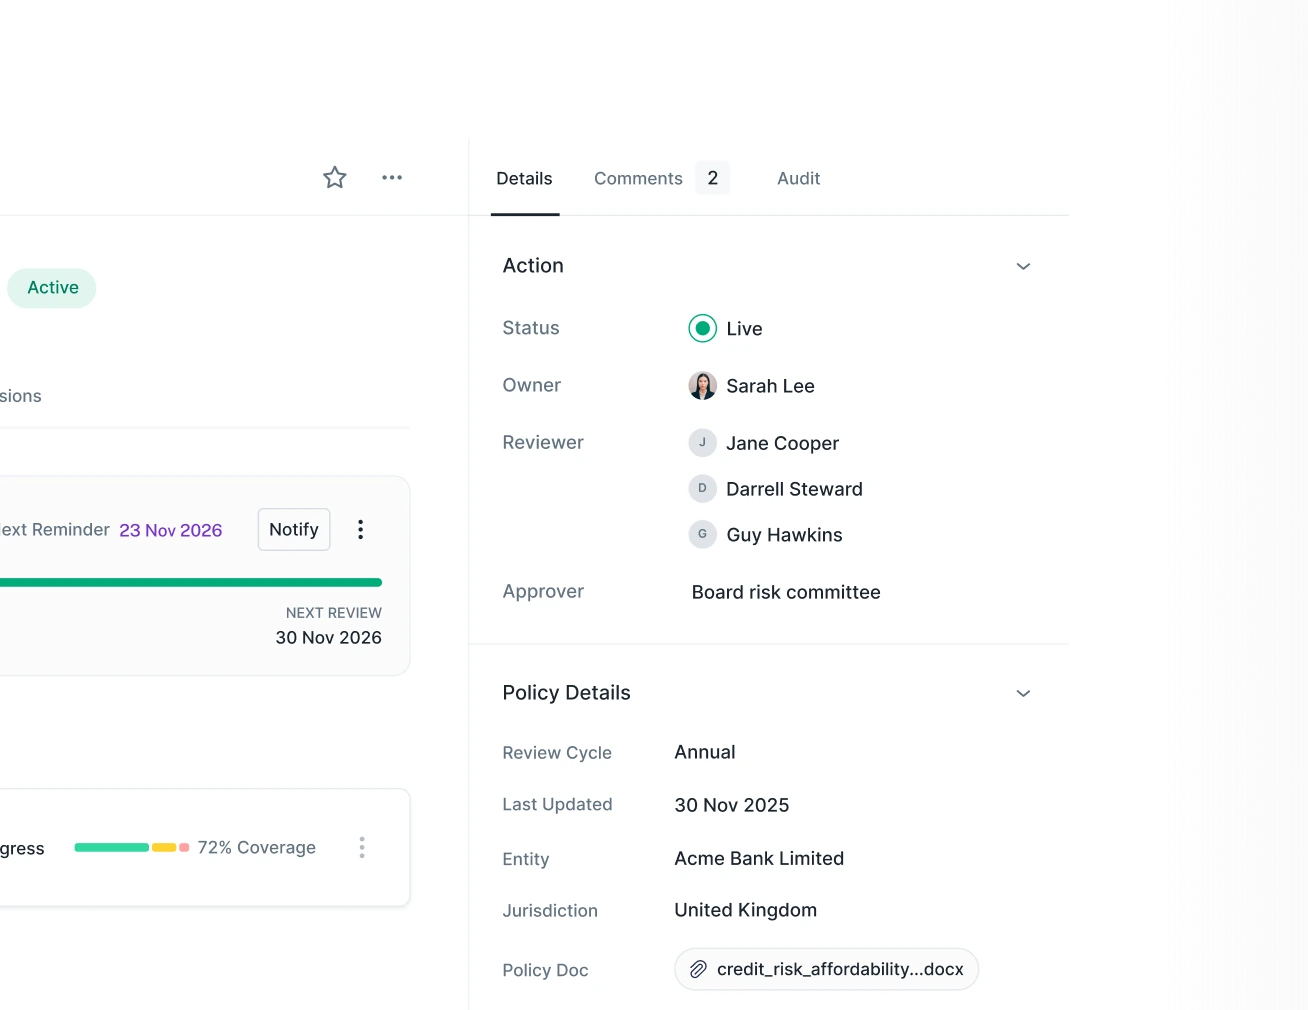
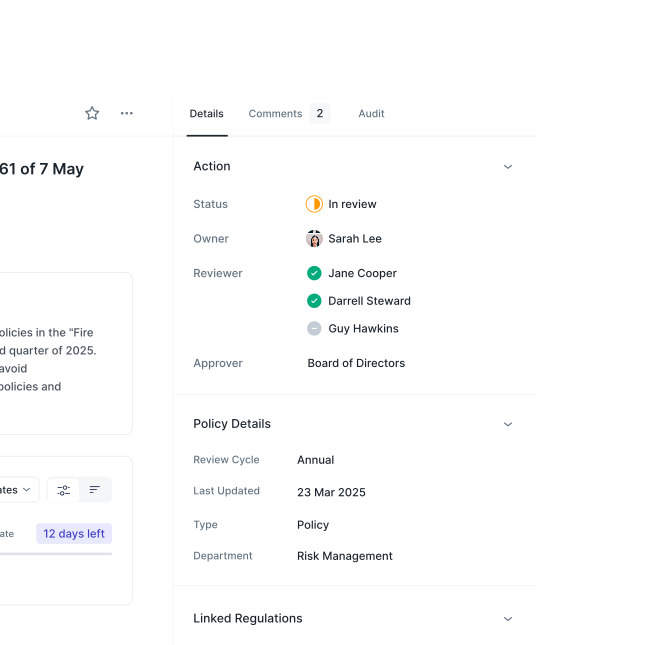
Owners, approvers, entities, jurisdictions and review cycles sit on every policy, with version history and regulatory deadlines on one timeline.
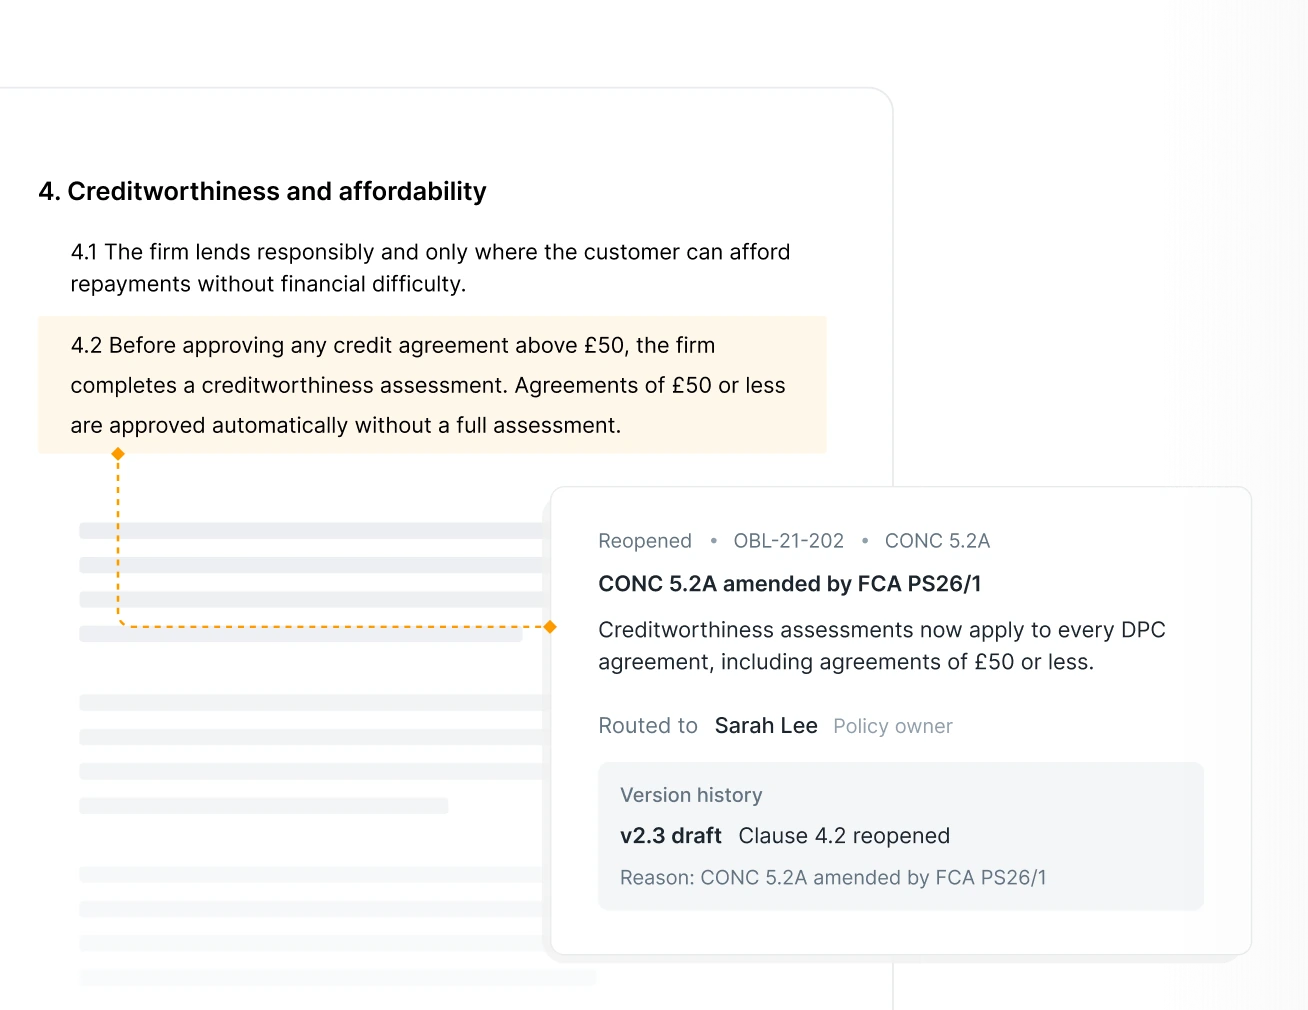
When a regulation changes, only the affected clauses are reopened and routed to the owner, with the change and its reason recorded in version history.
Agent flags the amendment and scopes it to your licences.


Agent extracts the obligations. An expert verifies each one.


Agent maps each obligation to your policies and controls, and flags the gaps.


Your team reviews, remediates and approves. The decision stays with you.

Agent detects the amendment and finds the affected policies.
Agents re-map the affected clauses. A reviewer checks the reasoning.
Agent assesses coverage and drafts a fix for each gap.
Your approver signs off the fix. The decision stays with you.
Security controls independently audited against the AICPA trust criteria.

Certified to the international standard for information security management.

Personal data processed in line with UK and EU GDPR.


Every decision, sign-off and accountability stays with your team, on the record.
Interviews with 27 senior risk, compliance and AI governance leaders, advised by the University of Glasgow and Oxford Martin School.
Read the report →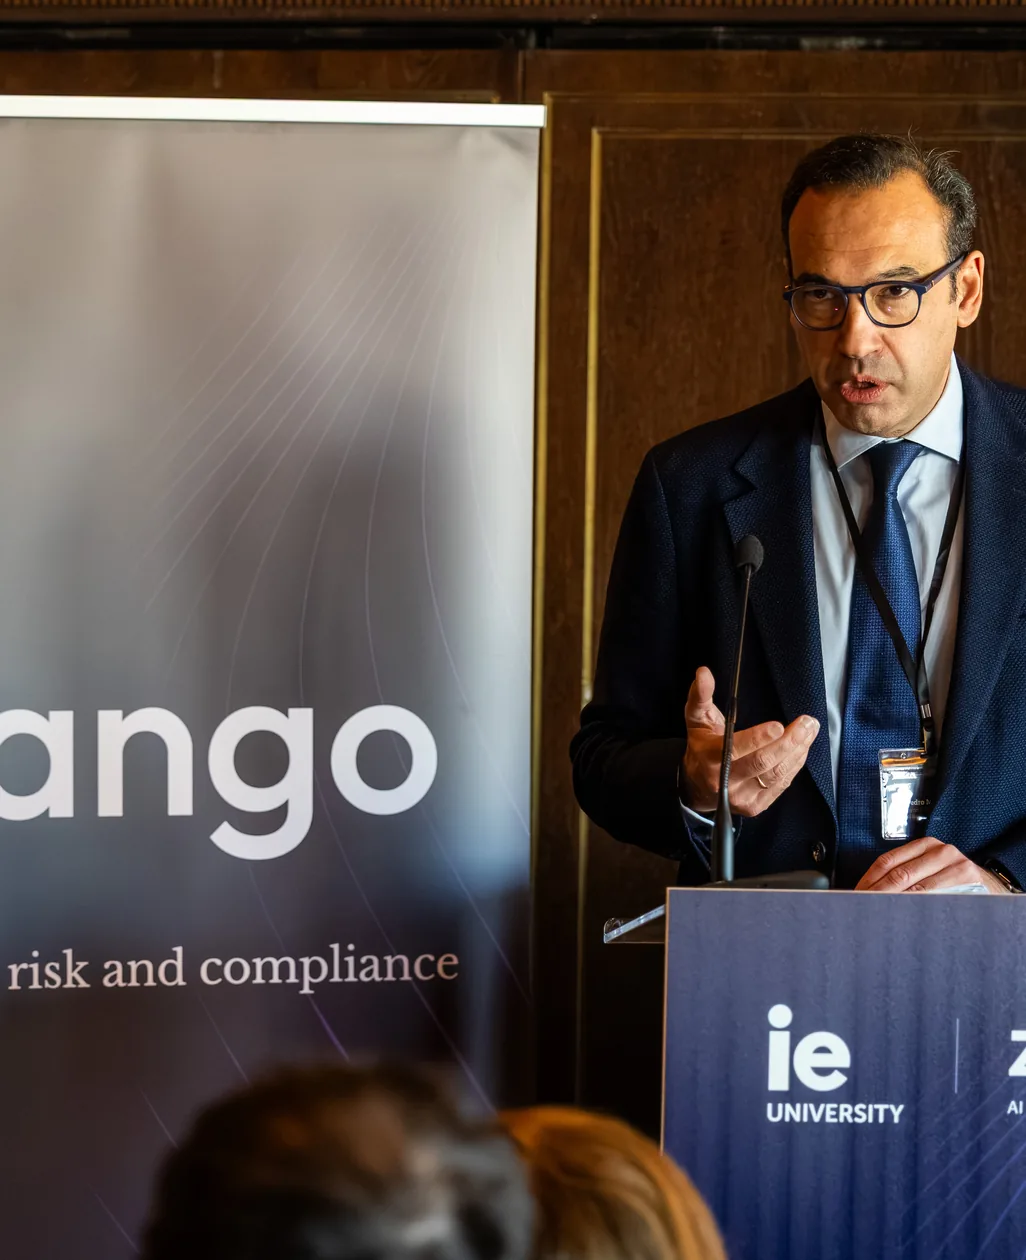
The ECB, Banco de España and Spain's leading banks on governing AI at scale. Hosted with IE University.
Read the recap →Policy governance software keeps your policies owned, reviewed and aligned to the regulations they must meet. Zango maps every policy to its regulatory obligations clause by clause, records owners, approvers and review cycles, and keeps the mapping live as regulation changes, so the next policy review starts from a current position.
A policy gap analysis checks whether your policies meet each regulatory obligation and identifies where they fall short. In Zango, agents run the analysis clause by clause and rate each obligation adequate, partial or gap, with the matched clause and reasoning recorded so second-line reviewers can challenge each finding.
Zango's agents read each policy and each obligation section by section and match them at clause level, using retrieval over a domain-specific regulatory corpus. Each match shows the policy clause, the criterion it meets and the reasoning, so reviewers can confirm or correct the mapping in seconds.
A consultant-led gap analysis is a one-off project that dates as soon as regulation changes. Zango keeps the policy-to-obligation mapping live, so every review starts from a current gap analysis. Clients report a 7x return on investment by replacing consultant spend, and the capability stays in-house.
Zango breaks each obligation into core criteria. Adequate means every core criterion is met by a clause in your policy, partial means some are met, and gap means none are. Best practice expectations are assessed separately, so regulatory requirements and good practice are reported distinctly.
Because each policy is linked to its obligations, Zango detects the change automatically. Agents flag the affected clauses, route them to the policy owner and suggest a fix within 48 hours, and the change and its reason are recorded in the policy's version history.
No. Zango's agents draft suggested clause text for each gap. The policy owner accepts or edits the wording, the approver signs it off, and every step is recorded. Your policies change only when your people approve them.
Each policy in Zango has a named owner, reviewer and approver. Suggested fixes route to them in order, nothing is published without sign-off, and maker-checker approval is recorded against the policy with who, what and when.
Yes. Zango records every match, suggested fix, edit, approval and change of owner with who, what and when. You can show the state of any policy at any point in time, and export the evidence when an auditor or regulator asks.
Yes. Zango is SOC 2 audited and ISO 27001 certified, processes personal data in line with UK and EU GDPR, encrypts data in transit and at rest, and supports single sign-on with role-based permissions. Every change is recorded with who, what and when.


We use cookies to provide you with the best possible experience. They also allow us to analyse how the site is used so we can keep improving it for you. See our Cookies Policy
